




Purplemet Cloud 1.38.0 New Features
Purplemet Cloud 1.38.0 is now available! This new version features several updates and enhancements compared to the previous version, as described hereafter.
Emerging Threats – Purplemet Alerting in the Platform
Purplemet Alerting watches public security news for emerging threats — zero-days, active exploitation, public proofs of concept, vendor advisories — and warns you when one concerns a technology detected in your inventory. Until now, these alerts were only sent by email. They now live in the platform too, in a dedicated Emerging Threats view, so no alert is ever lost in a mailbox.
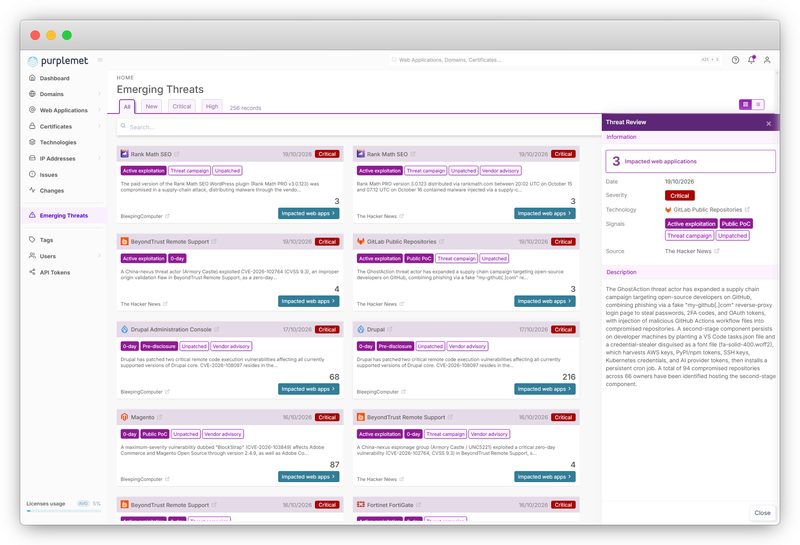
A new Emerging Threats entry in the main menu, open to every role, lists each threat as a card showing the technology, severity, signals (0-day, active exploitation, public PoC…), source and number of impacted web applications, with tabs to focus on new, critical or high threats. Opening a card displays the full details in the Threat Review pane, and one click on the impacted count takes you to the affected web applications.
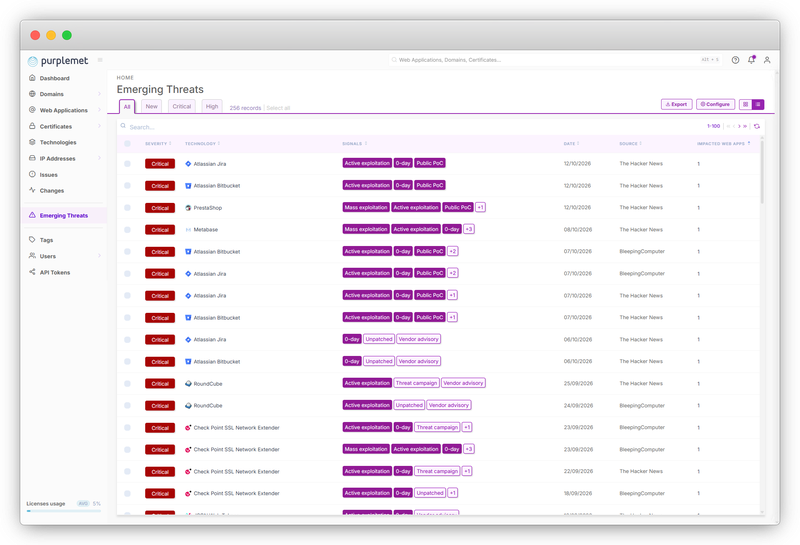
A list view with configurable, sortable columns and CSV export sits beside the cards, and both views use the same search language as the other inventories.
Emerging Threats – Restricted to Your Perimeter
A threat is shown only when its technology is detected on at least one web application you can see: the whole company for an unrestricted user, or the web applications carrying your tags for a tag-restricted user. Nobody is ever told about web applications outside their scope.
- Impacted web applications are counted on that same perimeter, so a card, an alert email and the Technologies inventory always give the same figure.
- Technologies detected only on disabled or deleted web applications are not counted.
- Alert emails follow the same rule: each one is now built for a single recipient, from that recipient’s own perimeter.
Emerging Threats – Alerting Preferences
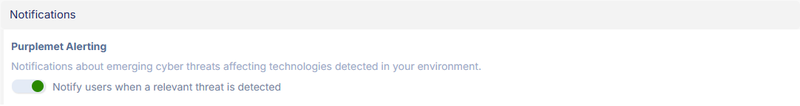
Each subscription and each user can now decide whether alert emails are sent. Administrators can turn alert emails on or off for the whole subscription and preset the choice for new accounts, while each user can follow that setting or choose to always or never receive alerts, without any impact on the Emerging Threats view, which always shows every threat in their perimeter.
API – Version 3.5.0
The API moves to version 3.5.0 and exposes the counts, filters and statistics behind the Overview, Web Applications and Technologies dashboards, each answered in a single request. The API now provides counts for web applications (by status, authentication mode and API type), certificates (by issues and weakness) and technologies (by category, technical debt, OpenSSF score and open CVEs or CISA KEVs). It also adds issue trends such as detected versus fixed issues over 12 months and the mean time to fix, plus a CSV export, new sort orders and a source filter for Emerging Threats.

